
Organizations can invest heavily in preventing cyberattacks and still face disruptions that bring critical operations to a halt. Preparing for such scenarios involves decisions about business priorities, financial exposure, and accountability that extend well beyond the security department.
With cyber resilience moving higher on the corporate agenda, security leaders are becoming more involved in discussions about how businesses can withstand attacks and limit operational disruption. As Theresa Lanowitz, Cybersecurity Industry Analyst at Omdia, puts it, "When we are breached, how does the whole organization coalesce to make sure that we lose as little business productivity as possible?"
Cybersecurity strategies are shifting toward resilience and recovery
Preventing unauthorized access, protecting systems, and detecting threats remain central to cybersecurity. Yet even mature security programs can't eliminate every vulnerability or guarantee that an attacker will never gain access. Organizations also need to understand how disruption could affect their operations and what it would take to restore critical services.
"In that event, you must have the infrastructure, capabilities, and processes in place to recover nearly instantly. The days of thinking we can recover in two weeks simply don’t fly anymore," says Rick Orloff, VP and CISO at Everpure. Meeting those expectations requires a more integrated approach to cyber resilience, with built-in security, connected threat detection, and coordinated response extending into enterprise storage infrastructure.
Andre Troskie, EMEA Field CISO at Veeam, argues that security strategies must account for attackers getting through existing defenses, with recovery capabilities designed to support operations after an incident. "People might get in, so we need to be resilient so we can bounce back when something bad happens. And we need to bounce back at scale and at speed," he says. Beyond cybersecurity planning scope, organizations must consider which business functions depend on vulnerable systems, how long those functions can remain unavailable, and what alternatives exist during an extended outage. The answers depend on knowledge and decisions that security teams don't always control.
Cyber resilience is blurring lines of accountability
As resilience becomes more closely connected to business continuity, responsibility for it is becoming harder to assign to a single executive or department. Security teams oversee cyber risks, IT departments manage infrastructure, and operational leaders are accountable for the business processes those systems support. An effective response depends on coordination across these functions.
Nicholas Currie, Principal Consultant at Beyond Blue, has observed this requirement in his work with financial-services organizations in the UK, and came to the conclusion that many companies haven't established a mature, clearly defined function responsible for resilience across the business. "There isn't a single function that tends to occupy that role," he explains. In many of the organizations he advises, ultimate responsibility sits with the chief operating officer, even though cyber and technology risks account for much of the resilience work. CISOs may be expected to strengthen the organization's preparedness without having direct authority over every system, process, or resource involved in recovery.
This distribution of responsibility also changes the board's role in overseeing cyber risk. Rob Labbé, CEO and CISO-in-Residence at the Mining and Metals ISAC, argues that boards should establish acceptable risk levels and hold management accountable when the organization exceeds them. "They should be looking at management and going, 'That risk is outside of our risk tolerance. Fix it,'" he says.
The financial cost of downtime is reshaping security investment
Establishing accountability also requires executives to understand the business consequences of cyber disruption. Security teams can identify vulnerabilities and recommend improvements, but obtaining funding often depends on how effectively they communicate the potential impact to management. Todd Wade, a veteran CISO, has seen how difficult this can be in practice. "There's an old irony here that if you want your security budget to increase, go through a ransomware attack," he says.
The financial consequences of an incident can suddenly bring urgency to security recommendations management previously rejected, even when the underlying risks were already known. Brian Fricke, CISO at AutoNation, advocates making those potential consequences clear before a disruption occurs and involving business leaders in assessing the risks. "I think the better we are at framing the technology risk to each line of business executive and empowering them to be a part of that conversation, you start to get that top-down support," he says.
For operational leaders, understanding the potential cost of downtime provides a basis for setting recovery priorities, too. They can establish realistic recovery objectives by assessing how long critical business processes can remain disrupted and the losses associated with prolonged outages.
Why incident preparation should extend into the boardroom
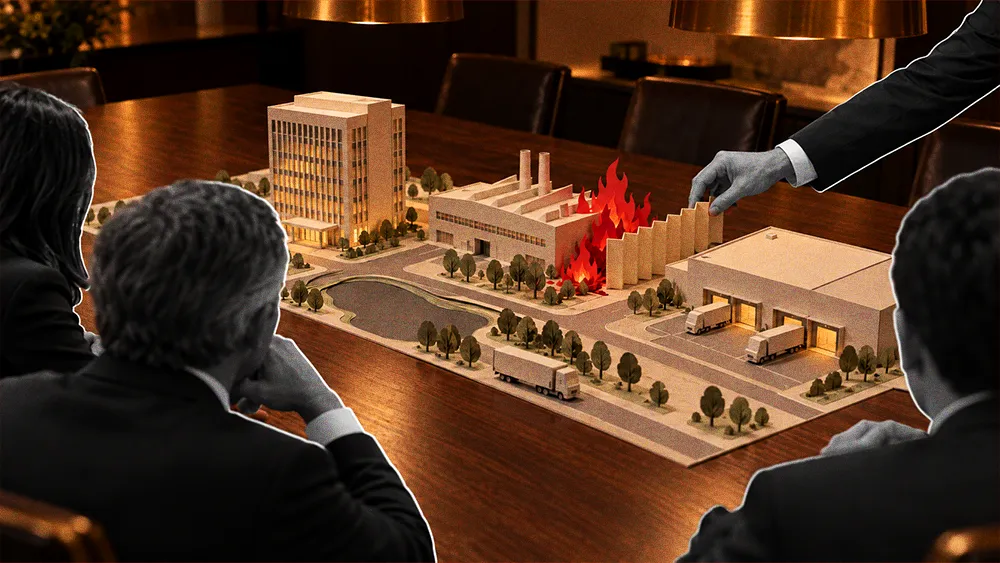
Financial planning can establish priorities, but an organization's preparedness also depends on how its leaders respond when an incident occurs. Cyberattacks create competing demands for information, decisions, and technical action, often before security teams have established the full extent of the damage. Without clear procedures, executives may repeatedly request updates while security teams are attempting to investigate and contain an attack.
Chris Patteson, Director of Cybersecurity, GRC, at a large pharmaceutical manufacturing organization, believes tabletop exercises should involve executives and board members alongside technical teams. These exercises allow leadership to work through potential scenarios, clarify decision-making responsibilities, and agree on communication procedures before an emergency unfolds. "When this happens, we're going to be busy working this incident. We will give you an update every six hours," Patteson says, illustrating how establishing expectations in advance can reduce friction and allow security teams to focus on responding to the threat.
Cyber resilience depends on decisions made well before a crisis. Executives need to understand their organization's critical dependencies, establish clear accountability, and ensure that security priorities reflect the consequences of business interruption. The ultimate value of cybersecurity comes from its contribution to the organization and the outcomes it needs to achieve.